Endpoint protection built for homes and small teams without a security department. It watches every machine, stops threats at the deepest level, explains what it finds in plain language, and answers your security questions like a colleague would.
Curious what the internet can see about you? Try our free 60-second check →Pick an incident from our own adversarial testing. Press play and Sentry North walks the attack stage by stage, fires the detection that catches it, and explains every decision in plain language as it happens.
A lightweight agent on every machine, whether that is one laptop at home or a whole office of them. It watches how programs behave, catches threats before they spread, and explains what it found in words you understand. Detection runs entirely on the machine.
Every alert arrives with what ran, what it touched, and why it was flagged. The technical evidence sits underneath for anyone who wants the depth. No codes to look up, no dashboards to decode.
Every alert arrives with the full attack story in plain language: what ran, what it touched, why it was flagged. The technical evidence sits underneath for anyone who wants the depth.
A built-in assistant your team can talk to. It triages alerts in real time, turns alert storms into single investigations, answers security questions, and walks you through hardening your systems.
Most tools apply the same rules to every computer. Sentry North watches how each machine normally behaves and builds its own baseline, so it flags what is genuinely out of place on that host.
Telemetry describes threat behaviour, never your files or your identity.
Four stages from raw endpoint events to a human-readable threat explanation. Each stage runs on its own. Detection and response never require the cloud.
Every meaningful action a program takes is observed in real time, on the endpoint itself, across Windows and Linux. Nothing is shipped to a vendor cloud to be understood.
Related events across your systems are connected into one threat signal. Noise is filtered out before you ever see it.
The assistant classifies threats and collapses alert storms into single investigations. Obvious threats are handled automatically; ambiguous ones go to a human.
Real-time protection kills malicious processes, quarantines files, and blocks network connections. Canaries catch encryption early.
AI-powered attacks are here now. Signature-based tools react after the damage is done. Sentry North acts at the moment of detection, on your machines, in language your team can read.
The assistant aggregates alerts into single investigations. Before anything destructive happens, multiple independent models must agree. If they disagree, a human decides.
Detection and response execute on the endpoint, so your protection holds on degraded links and isolated networks. The assistant lights up when you connect. Your security does not depend on it.
No codes to look up, no dashboards to decode. Every alert tells you what ran, what it touched, and why it matters. Built for teams without a dedicated analyst.
Why was this flagged? What does this threat mean? How do I lock this down? Your assistant answers in plain language, on any machine it protects, and walks you through hardening steps you can follow.
Most endpoint security tools are cloud-first: detection logic, threat lookups, and telemetry flow through vendor infrastructure. Sentry North runs the important parts on your machines.
The system is built so there is nothing to hand over. Telemetry describes threat behaviour, never your files, your identity data, or your browsing history.
Every malware sample in our adversarial testing to date was detected, with zero false positives. All 15 MITRE ATT&CK tactics and all 64 techniques below are covered, and full detection goes live with early access, which is coming soon.
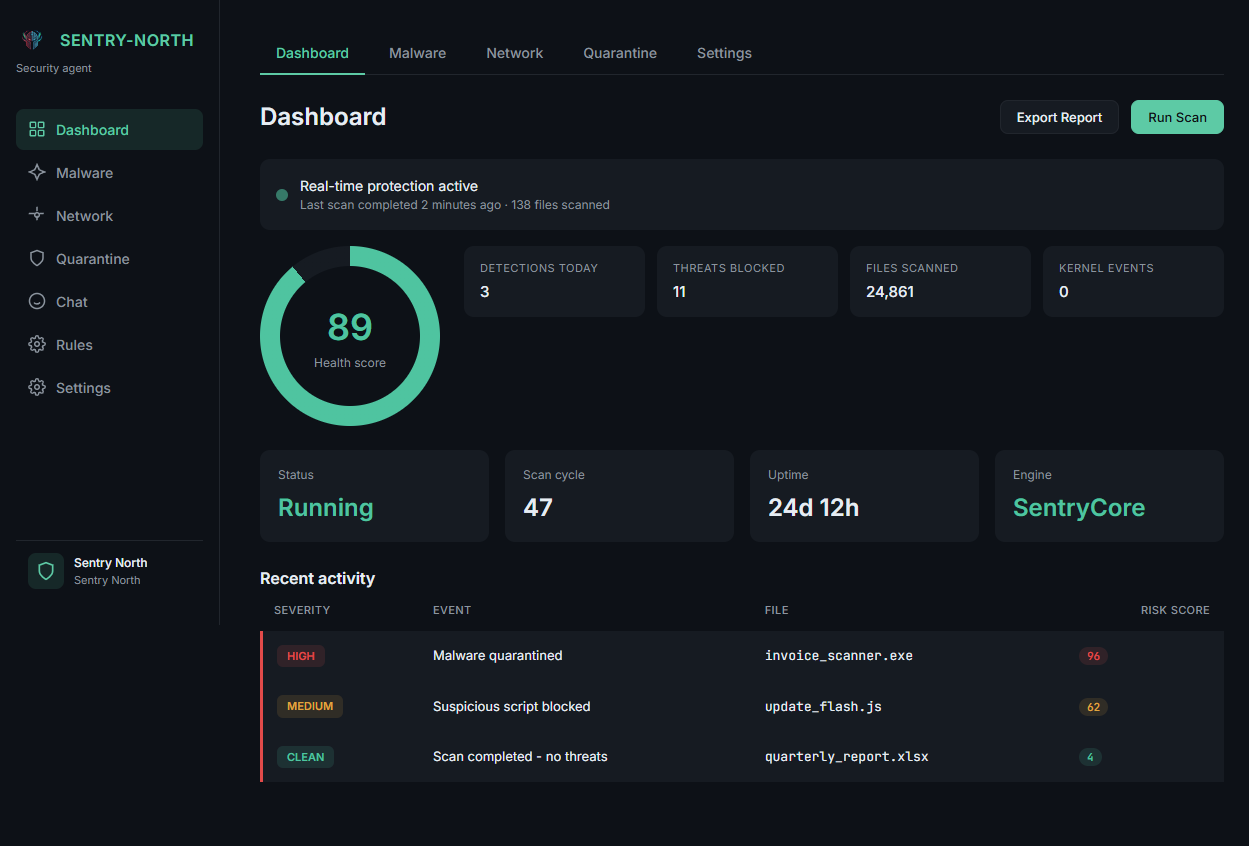
The Sentry North console shows every threat as a chain of evidence. Open any detection and you see the full process tree, the connections it made, the files it touched, and its MITRE mapping, all in real time.
Run our free 60-second check from your own browser. It looks at the doors on your connection, what your address says about you, what your browser reveals, and whether your password has appeared in a breach. Nothing is stored. Nothing to install.
Most small businesses never hire a security person. The job lands on whoever has the least room to say no, and they deserve a tool that speaks plainly to them.
You run the business and ended up doing the IT. Five to a hundred people, no security hire, and no time to become one.
The office manager it landed on, along with every other job. You want to know what actually matters, in words that make sense.
You are the whole IT department, plus five other things. Sentry North is the second set of eyes that never sleeps.
If all you have is your own machines, you get the same engine. No stripped-down home edition and no minimum number of devices.
Every tier runs the full engine. Service scales with you.
Larger than this? Talk to us about a fleet quote.
Meet the people behind Sentry North.
Leads product strategy, partnerships, and customer-facing operations. Designs the research methodology and adversarial testing behind our detection claims.
Leads technical architecture and detection engineering. Built Sentry North's detection systems: the on-device sensor, the multi-layer scanner pipeline, and the AI triage engine with safety verification.
Early access is coming soon. Whether it is your own computer or your company's fleet, join the waitlist to be first in line, or request a demo and see the system in our lab.